 BerryCade
10. Logs & Reports (Logs & Relatórios)
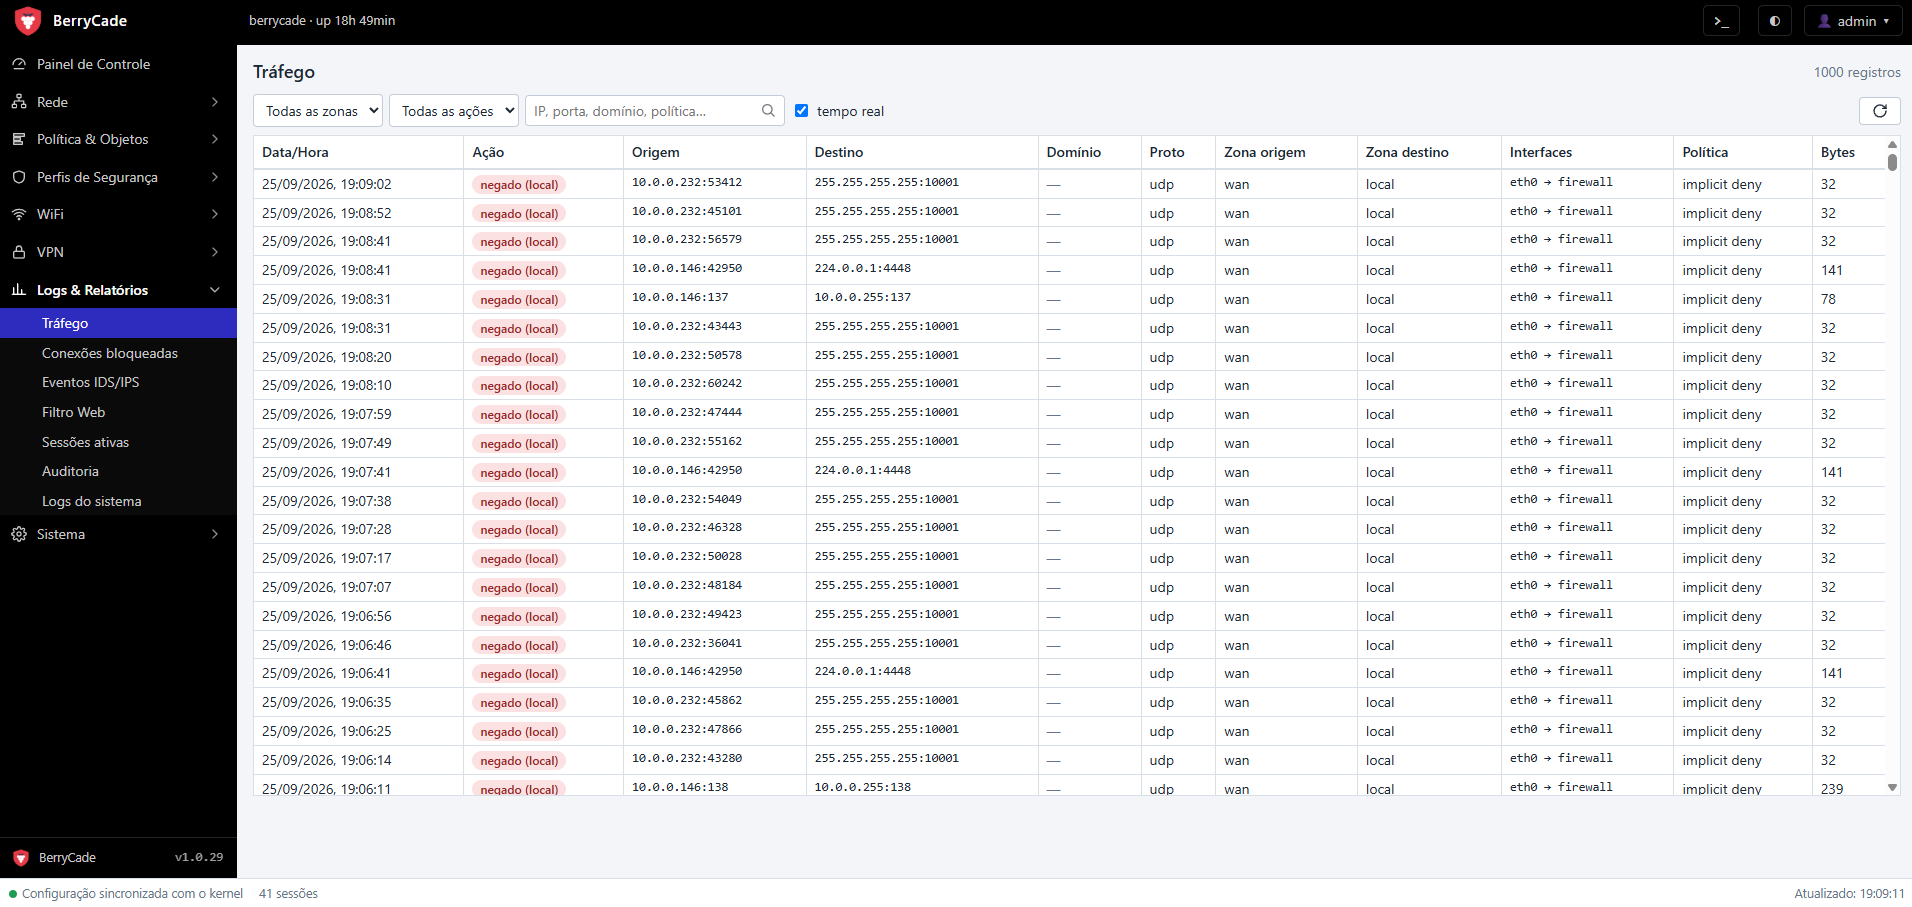
Figure 15 — Traffic screen (Logs & Relatórios › Tráfego)
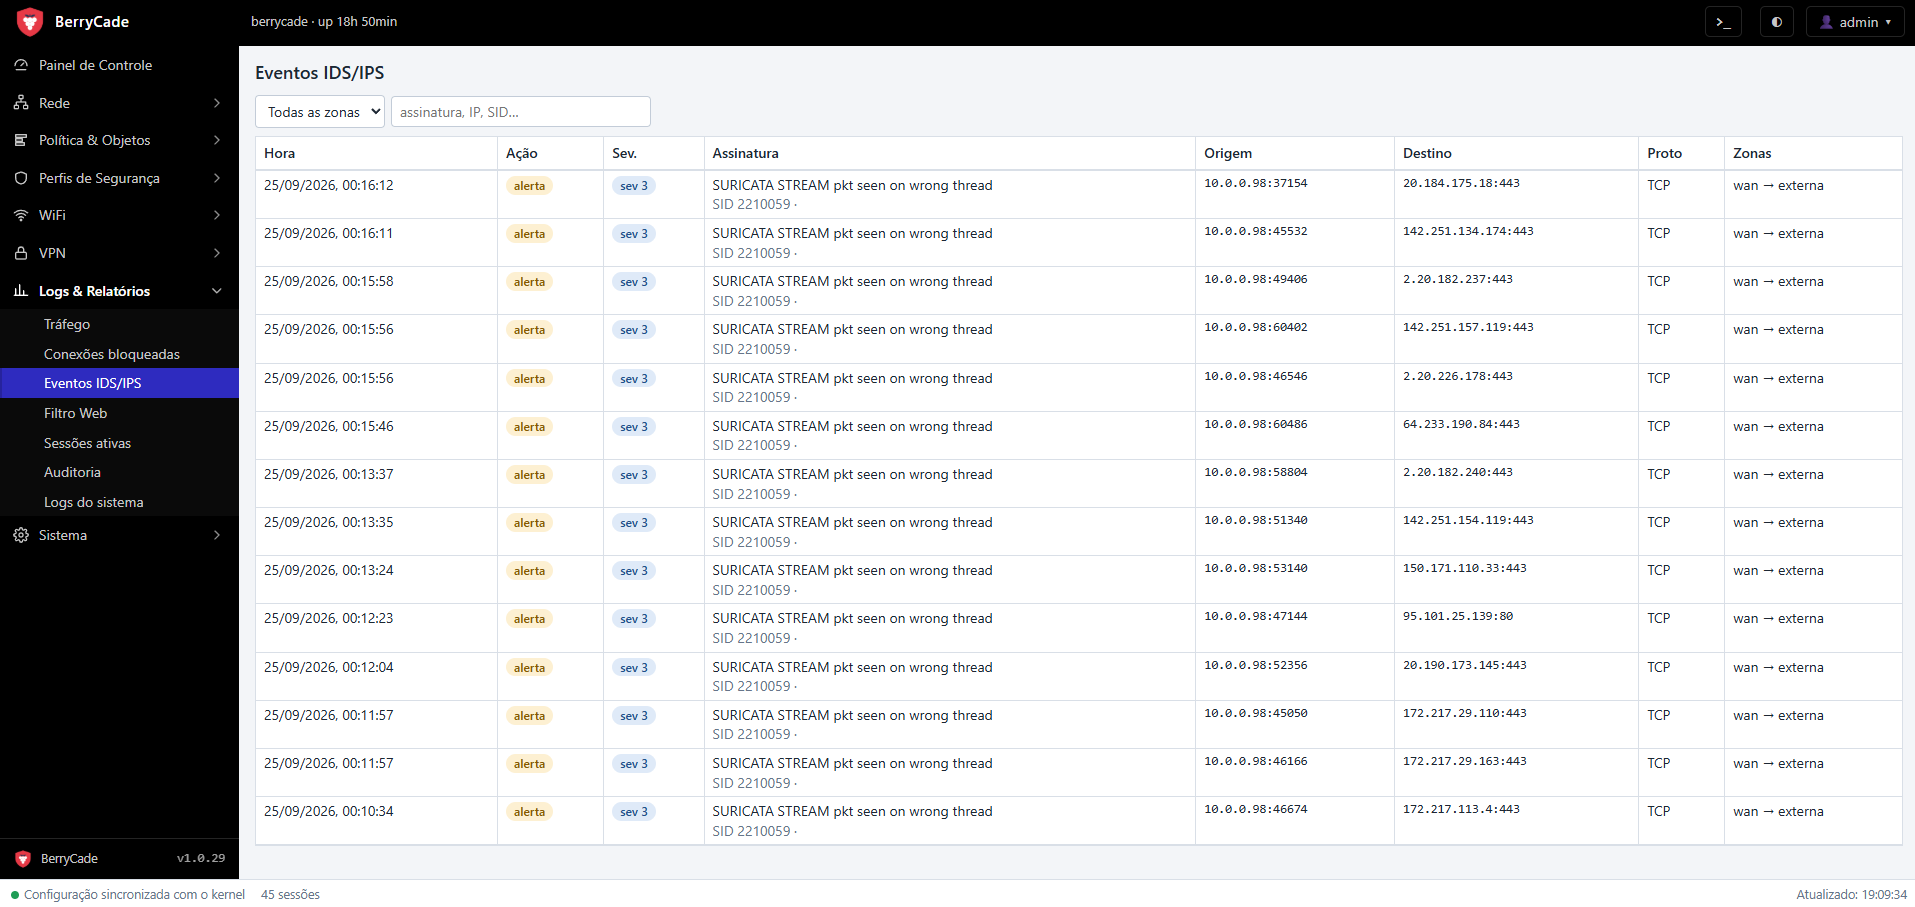
Figure 16 — IDS/IPS Events screen (Logs & Relatórios › Eventos IDS/IPS)
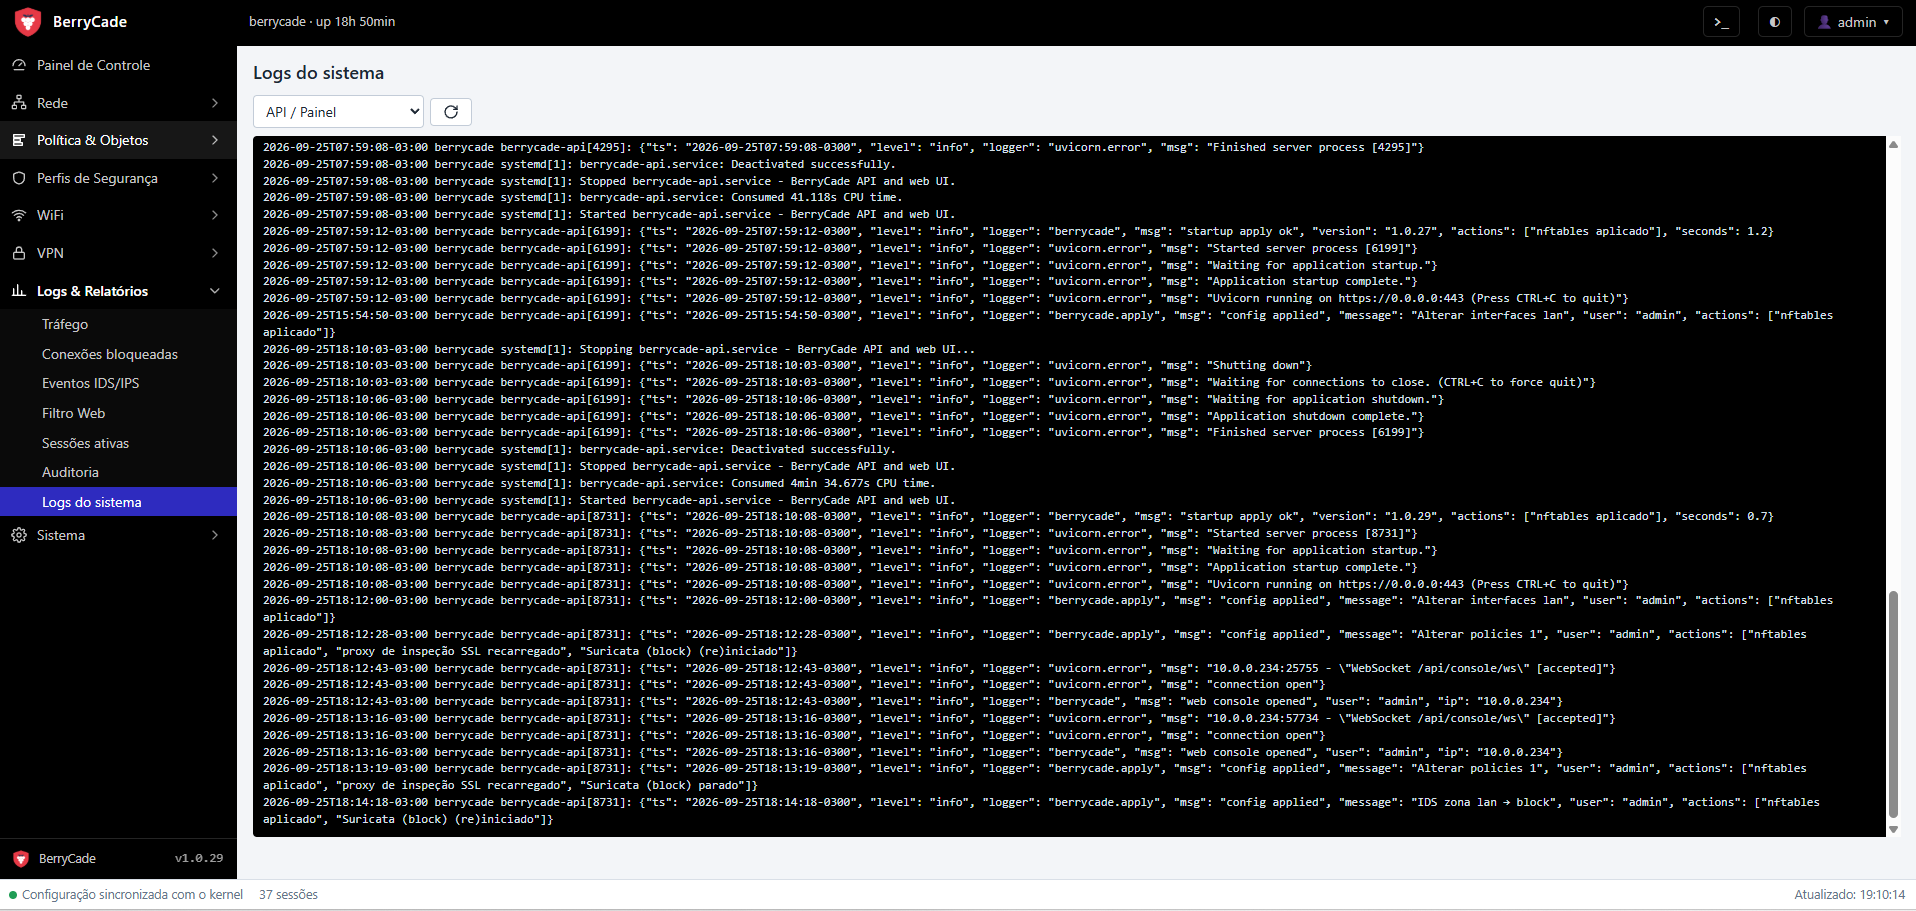
Figure 17 — System Logs screen (Logs & Relatórios › Logs do sistema)
| Screen | Contents |
|---|---|
| Tráfego (Traffic) | Sessions allowed by policies that have logging enabled, filterable by zone. |
| Conexões bloqueadas (Blocked connections) | Traffic dropped by the policies and by the implicit deny. Right-clicking creates an address object from the source. |
| Eventos IDS/IPS (IDS/IPS events) | Suricata alerts and blocks, with signature, category and severity. |
| Filtro Web (Web filter) | Access monitored and blocked by the web filter profiles. |
| Sessões ativas (Active sessions) | Connections in progress (protocol, source, destination, state, policy, bytes and expiration). |
| Auditoria (Audit) | All administrator changes and logins: date/time, user, action and details. |
| Logs do sistema (System logs) | Service logs (network, DNS/DHCP, PPPoE, IPsec, IDS, panel, etc.), chosen from the list. |